Vulnerability Management
Automatic binary SBOM scanning for public and private vulnerabilities, to comply with regulations and assure product security.
- Automotive cybersecurity
- Security compliance
- SBOM scanning
- B2B SaaS
- 0→1 Product
- Design system
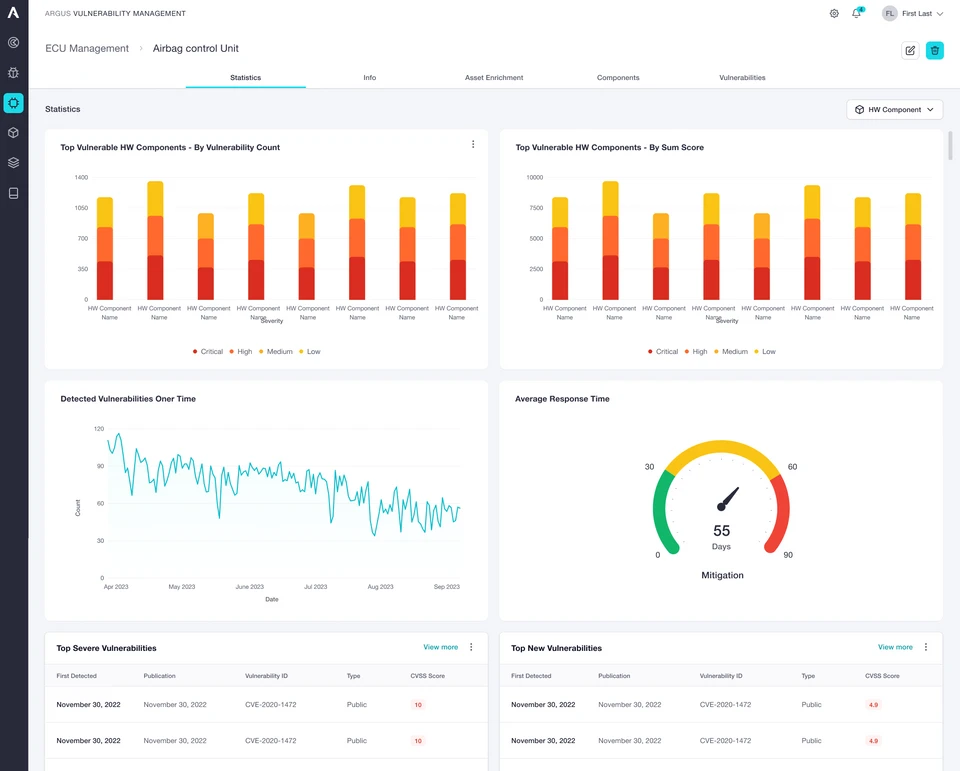
- Product
- Binary SBOM scanning for automotive security compliance
- Industry
- Security compliance
- My role
- UX Lead, end to end, including a new design system
UX Lead for a newly built product, responsible for end-to-end design and creating a new design system. Led improvement of main user flows after gaining Continental as first major client.
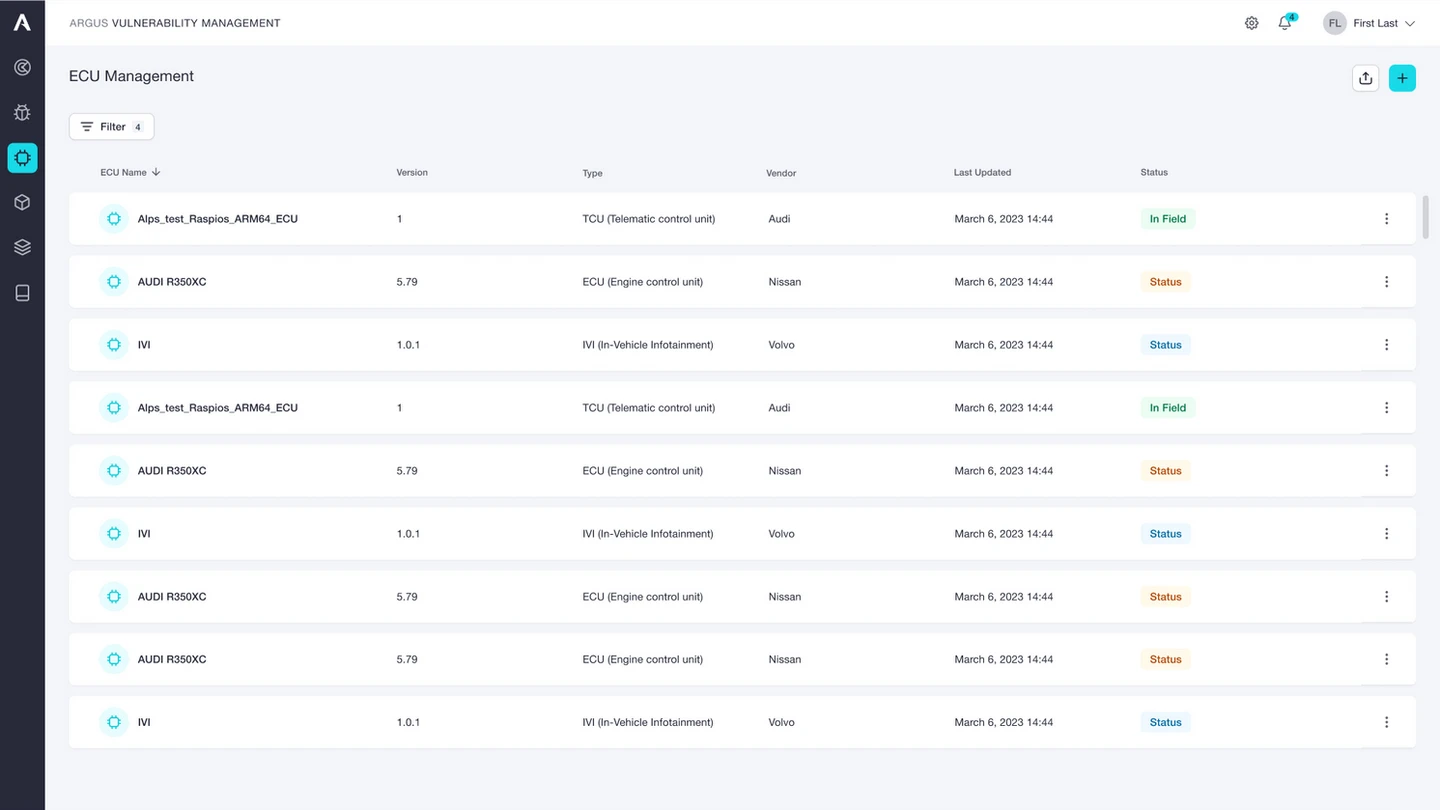
ECU management
Every ECU in one list
Version, type, vendor and status for every ECU.
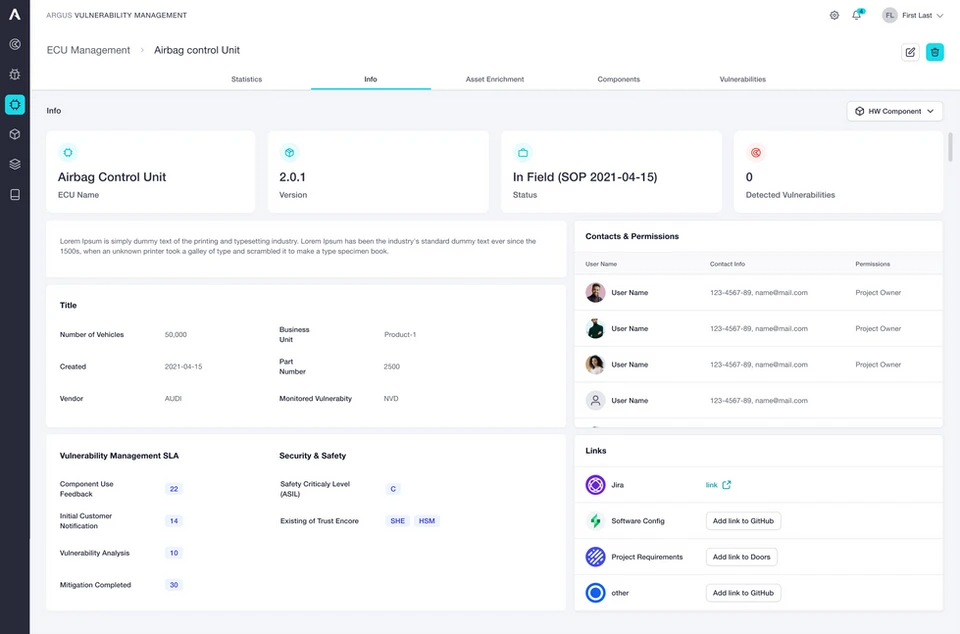
ECU details
An ECU's info page
Version, status and open vulnerabilities at the top, then contacts, permissions and links.
Challenge
For OEMs and Tier 1 manufacturers, the platform overwhelmed users as the data grew, forcing them to work across several tabs and side panels.
Decision
An updated information architecture and navigation flow, a role and task analysis, and a UI built on a new design system for cross-platform use.
Impact
- After the product gained Continental as its first major client, I led the improvement of its main user flows.
Standards and references
- CISA — Software Bill of Materials (SBOM)Background on the SBOM practice the scanner automates.